If you manage a remote cloud VPS, home NAS, or Raspberry Pi server using a traditional username and password over Secure Shell (SSH), your server is under continuous automated attack. Internet botnets scan the IPv4 address space 24 hours a day, executing millions of automated dictionary password guesses against port 22. Transitioning to cryptographic SSH keys not only eliminates brute-force vulnerabilities entirely, but also streamlines your workflow with instant, passwordless logins.
How Asymmetric Public-Key Cryptography Works
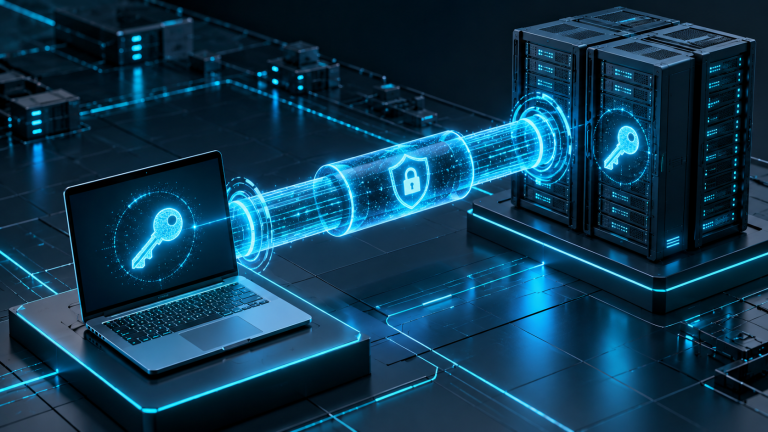
SSH key authentication utilizes an asymmetric mathematical keypair comprising two mathematically linked cryptographic files:
- Private Key (
id_ed25519): Stored exclusively on your personal client computer. It must remain strictly confidential and never shared with anyone. - Public Key (
id_ed25519.pub): Uploaded to the remote server and appended to its~/.ssh/authorized_keysfile. Anyone can see this key without compromising security.
When you initiate a connection, the server generates a random cryptographic challenge, encrypts it with your public key, and sends it to your machine. Your private key solves the mathematical challenge and responds with the signature. Authentication occurs in milliseconds without a single password character traveling across the network.
Step 1: Generating a Modern Ed25519 SSH Keypair
Legacy RSA 2048/4096-bit keys have been superseded by Ed25519, an elliptic-curve algorithm that provides superior cryptographic security, faster handshakes, and a compact key size. Open PowerShell (Windows) or Terminal (macOS/Linux) and execute:
ssh-keygen -t ed25519 -C "your_email@example.com"Press Enter to accept the default file location (~/.ssh/id_ed25519). When prompted, enter a strong passphrase to encrypt your private key at rest on your local disk.
Step 2: Copying Your Public Key to the Remote Server
On macOS and Linux:
Use the automated ssh-copy-id utility:
ssh-copy-id username@remote-server-ipOn Windows PowerShell:
Execute this single-line command to pipe your public key into the server’s authorized keys file:
type :USERPROFILE.sshid_ed25519.pub | ssh username@remote-server-ip "cat >> ~/.ssh/authorized_keys"Step 3: Hardening SSH Daemon to Disable Password Logins Completely
Once you verify that you can log in with your SSH key without entering your server password, lock down the server’s SSH configuration file:
- On the server, edit the SSH daemon config:
sudo nano /etc/ssh/sshd_config - Locate and set the following hardening directives:
PasswordAuthentication no ChallengeResponseAuthentication no PubkeyAuthentication yes PermitRootLogin prohibit-password - Save and restart the SSH daemon:
sudo systemctl restart sshorsudo systemctl restart sshd.
Your server is now completely immune to password brute-force bots.