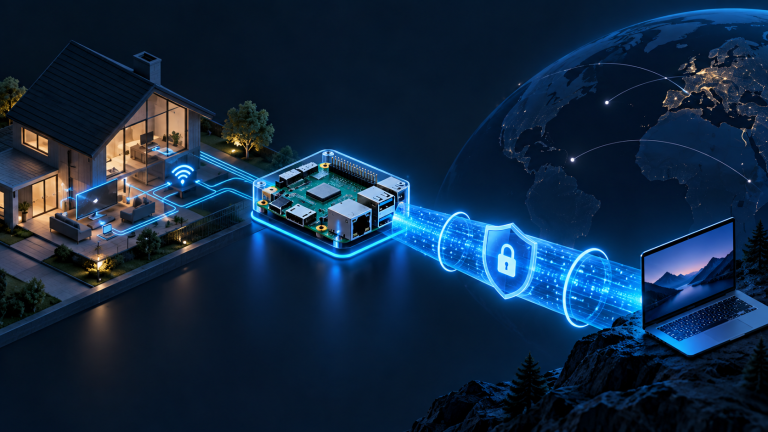
Public Wi-Fi networks in airports, hotels, and cafes expose your browsing traffic to packet sniffing, DNS hijacking, and man-in-the-middle attacks. While commercial VPN services route your traffic through remote servers, they cannot provide secure access back into your home storage drives, smart home hubs, or local servers. Setting up your own personal WireGuard VPN on a lightweight home server—such as a Raspberry Pi or repurposed desktop PC—delivers the ultimate combination of privacy, control, and zero subscription costs.
- Why Choose WireGuard Over Legacy OpenVPN or IPsec?
- Hardware and Network Prerequisites
- Step 1: Installing PiVPN with the WireGuard Protocol
- Step 2: Configuring Port Forwarding on Your Home Router
- Step 3: Creating and Exporting Client Profiles
- Step 4: Testing Your Encrypted Tunnel
- Official Sources & Technical References
Why Choose WireGuard Over Legacy OpenVPN or IPsec?
For over a decade, OpenVPN stood as the de facto standard for self-hosted VPN tunnels. However, OpenVPN relies on hundreds of thousands of lines of code, complex cryptographic handshakes, and noticeable battery consumption on mobile devices. WireGuard modernizes network tunneling with distinct advantages:
- Minimalist Attack Surface: WireGuard comprises fewer than 4,000 lines of clean C code, making it drastically easier to audit for security vulnerabilities compared to OpenVPN’s 100,000+ line codebase.
- State-of-the-Art Cryptography: By utilizing fixed modern primitives like Curve25519 for key exchange, ChaCha20 for encryption, and Poly1305 for authentication, WireGuard eliminates obsolete cipher negotiation vulnerabilities.
- Instant Roaming & Connection Speed: WireGuard operates over UDP. When your smartphone switches from home Wi-Fi to 5G cellular, the connection does not drop or require renegotiation; the tunnel maintains seamlessly without draining your battery.
Hardware and Network Prerequisites
Before initiating the installation, ensure you have the following prerequisites prepared:
- A dedicated machine running 24/7 (Raspberry Pi 3B+, 4, 5, or any mini-PC running Debian, Ubuntu, or Raspberry Pi OS).
- A wired Ethernet connection from the server to your primary home router for maximum stability.
- Administrative access to your home broadband router to configure port forwarding.
- A Dynamic DNS (DDNS) hostname (such as DuckDNS, No-IP, or Cloudflare API) if your Internet Service Provider assigns a dynamic public IP address.
Step 1: Installing PiVPN with the WireGuard Protocol
While WireGuard can be configured manually via configuration files, the open-source PiVPN utility simplifies client certificate management, firewall rules, and IP routing without bloat.
Open a terminal on your Linux server via SSH and execute the official installer:
curl -L https://install.pivpn.io | bashWhile the PiVPN documentation provides a convenient one-line installation script, best security practice when running remote scripts is to inspect the source code locally before execution:
curl -sSL https://install.pivpn.io -o install-pivpn.sh && less install-pivpn.sh && bash install-pivpn.shFollow the interactive setup wizard:
- Confirm the static local IP address of your host machine (e.g.,
192.168.1.150). - When prompted to select your VPN protocol, choose WireGuard.
- Select the default listening port (51820 UDP) or specify a custom high-range port.
- Choose a secure upstream DNS provider for connected clients, such as Cloudflare (
1.1.1.1) or Quad9 (9.9.9.9), or specify your local Pi-hole address for network-wide ad blocking. - Select whether clients will connect via your public IP address or your configured Dynamic DNS hostname.
Step 2: Configuring Port Forwarding on Your Home Router
Check your home router’s WAN IP address. If the WAN address begins with
100.64.x.x to 100.127.x.x (the RFC 6598 CGNAT range), your Internet Service Provider is sharing public IP addresses. Direct port forwarding on port 51820 UDP will not be reachable from external networks. In this case, contact your ISP to request a static public IP address, or use an overlay mesh VPN such as Tailscale (which operates on top of the WireGuard protocol without requiring open router ports).
To allow encrypted traffic to reach your internal WireGuard server from outside your local network, log into your router’s administrative dashboard and locate the Port Forwarding section:
- Service Name: WireGuard VPN
- Protocol: UDP (WireGuard strictly uses UDP; do not select TCP)
- External Port: 51820
- Internal Port: 51820
- Internal IP Address: The static IP of your Raspberry Pi (e.g.,
192.168.1.150)
Step 3: Creating and Exporting Client Profiles
Once installation finishes and your server reboots, generating client profiles takes seconds. In your terminal, run:
pivpn addEnter a recognizable name for the client (e.g., laptop-work or phone-mobile). To connect a smartphone or tablet:
pivpn -qrThis command renders an ASCII QR code directly inside your terminal window. Open the official WireGuard app on your iOS or Android device, tap the “+” button, select “Create from QR code”, and scan your screen. The tunnel profile imports instantly with cryptographic keys pre-paired.
When reviewing or editing your client configuration profile (
.conf), note the AllowedIPs directive:
- Full-Tunnel (Maximum Security on Public Wi-Fi): Setting
AllowedIPs = 0.0.0.0/0, ::/0routes 100% of your remote device’s internet traffic through your encrypted home connection, shielding airport or hotel browsing. - Split-Tunnel (Local LAN Access Only): Setting
AllowedIPs = 192.168.1.0/24routes only requests for your local home devices (e.g. NAS, home server) through WireGuard, while general web browsing uses your mobile cellular connection directly without latency.
Step 4: Testing Your Encrypted Tunnel
To verify that your VPN is routing traffic properly:
- Disconnect your mobile device from your home Wi-Fi and switch to cellular data.
- Toggle the WireGuard tunnel switch in the app.
- Open a browser and navigate to a public IP checker (e.g.,
https://api.ipify.org). The returned IP address should match your home broadband address, not your cellular carrier. - Test opening an internal home device (such as your router gateway at
192.168.1.1). If the page loads over cellular, your private tunnel routing is operating flawlessly.
Official Sources & Technical References
- WireGuard Official Technical Whitepaper (Jason A. Donenfeld) — Formal cryptographic protocol verification, state machine design, and Linux kernel implementation.
- PiVPN Official Open-Source Documentation — Automated deployment specifications, certificate management, and split-tunnel networking.
- IETF RFC 8439 — ChaCha20 and Poly1305 for IETF Protocols — Authenticated encryption with associated data (AEAD) cryptographic standard.
- IETF RFC 7748 — Elliptic Curves for Security (Curve25519) — Cryptographic key exchange standard utilized in modern WireGuard handshakes.