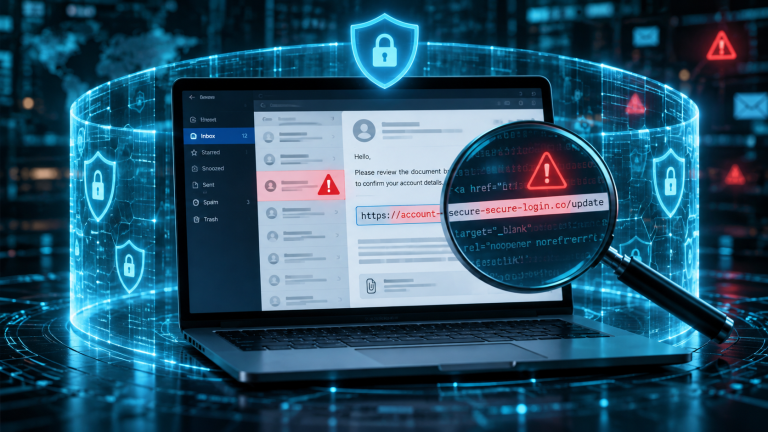
Modern phishing attacks have evolved far beyond crude spelling mistakes and Nigerian prince inheritance solicitations. Today’s threat actors deploy automated reverse-proxy frameworks like Evilginx, spoof authentic company subdomains, synthesize hyper-realistic executive voice notes, and leverage Unicode lookalike domains. To safeguard corporate and personal digital assets, you must adhere to these 5 non-negotiable rules of technical threat defense before clicking any inbound link or authorizing an authentication prompt.
- Rule 1: Inspect Full Sender Return-Path and Header Authentication Alignment (SPF, DKIM, DMARC)
- Rule 2: Detect Unicode Lookalike Domains and Punycode Homoglyph Exploits
- Rule 3: Inspect Hyperlink Target Destinations Manually Before Interaction
- Rule 4: Decouple Urgent Requests from Direct Communication Channels (Out-of-Band Verification)
- Rule 5: Implement Cryptographic Hardware Security Keys and Passkeys (FIDO2) to Neutralize Reverse-Proxy Toolkits
- Summary Checklist: The 5-Point Threat Defense Matrix
- Authoritative Standards & Industry References
- Sources & Further Reading
Rule 1: Inspect Full Sender Return-Path and Header Authentication Alignment (SPF, DKIM, DMARC)
Never rely on the friendly display name shown in your email client’s inbox list. Email headers consist of two distinct sender addresses: the Header From address (which email clients visually display) and the Envelope From (Return-Path) address used by mail servers to route delivery status notifications.
Follow this technical inspection process when evaluating any suspicious message:
- Examine the Raw RFC 822 Email Headers: In Gmail, click the three-dot menu and select Show original; in Outlook, open File > Properties > Internet headers.
- Verify SPF (Sender Policy Framework): Check whether the sending mail server IP is formally authorized by the domain’s DNS TXT record. A value of
spf=passindicates the originating IP is legitimate. - Validate DKIM (DomainKeys Identified Mail): DKIM attaches a cryptographic digital signature to the email header. Verify that the signature resolves with
dkim=passand that the signing domain corresponds exactly to the brand entity sending the notification. - Check DMARC Policy Alignment: DMARC ensures alignment between SPF and DKIM. If DMARC reports
dmarc=fail, the message has been spoofed and should be flagged immediately.
Rule 2: Detect Unicode Lookalike Domains and Punycode Homoglyph Exploits
Attackers exploit internationalized domain names (IDNs) by registering domains containing Cyrillic, Greek, or Latin lookalike characters (homoglyphs) that appear identical to standard English characters in modern web browsers.
For example, the Cyrillic small letter “а” (Unicode U+0430) is visually indistinguishable from the Latin “a” (Unicode U+0061), yet resolving this domain routes traffic to an entirely different attacker-controlled server.
- Inspect the Punycode Translation: When an international domain is registered, DNS resolvers translate it into a Punycode string prefixed with
xn--. If a link purporting to be a major bank or cloud provider begins withxn--in your address bar, it is a homoglyph spoofing attack. - Type Critical URLs Manually: Never follow inbound email hyperlinks to log in to high-value infrastructure (AWS, Cloudflare, banking, or password managers). Always open a fresh tab and navigate directly via a stored bookmark.
Rule 3: Inspect Hyperlink Target Destinations Manually Before Interaction
A standard hyperlinked anchor tag in HTML separates the visible anchor text from the underlying destination URL (the href attribute). Phishing emails frequently display authentic-looking anchor text (such as https://accounts.google.com/signin) while directing the underlying click event to an external malicious server.
- Hover to Reveal the Tooltip URI: Position your cursor over the link without clicking and inspect the status bar at the bottom-left corner of your email client or browser window.
- Analyze the Fully Qualified Domain Name (FQDN): Read URLs from right to left starting immediately before the first single forward slash (
/). Inhttps://accounts.google.com.attacker-domain.org/login, the actual destination host is attacker-domain.org, not Google. Subdomains can be customized infinitely by threat actors. - Beware of Legitimate Redirect Services: Attackers often abuse open-redirect parameters on legitimate marketing platforms (e.g., SendGrid, HubSpot, or Firebase dynamic links) to bypass basic automated spam filters.
Rule 4: Decouple Urgent Requests from Direct Communication Channels (Out-of-Band Verification)
Social engineering relies fundamentally on synthetic urgency. Phishing lures simulate account terminations, wire transfer deadlines, tax penalties, or compromised payroll records to induce panic and short-circuit analytical thinking.
- Enforce the Out-of-Band Principle: If an email, Slack message, or SMS purports to be from your CFO, an executive, or a core vendor requesting credential changes or funds disbursement, never reply within that thread or click provided verification links.
- Contact the Purported Sender via Independent Channels: Call the verified corporate phone extension, send a direct SMS over an established mobile number, or speak in person to authenticate the request before taking action.
Rule 5: Implement Cryptographic Hardware Security Keys and Passkeys (FIDO2) to Neutralize Reverse-Proxy Toolkits
Modern adversaries utilize automated adversary-in-the-middle (AiTM) reverse proxies like Evilginx to intercept login sessions in real time. When an employee enters their username, password, and six-digit authenticator TOTP code on a proxy site, the server relays these credentials to the real service, captures the validated session cookie, and hands it to the attacker, completely bypassing traditional two-factor authentication.
- Why FIDO2 / WebAuthn Stops Reverse Proxies: Hardware security keys (such as YubiKeys) and passkeys bind cryptographic authentication credentials directly to the exact origin domain registered in the browser’s address bar.
- Origin-Bound Cryptography: If an AiTM proxy presents a fake domain (e.g.,
login.microsoftonline.attacker.com), the security key signs the challenge using the attacker’s domain origin. When forwarded to the real service, the signature fails validation instantly, rendering credential interception impossible.
Summary Checklist: The 5-Point Threat Defense Matrix
| Rule | Threat Mechanism | Defensive Action |
|---|---|---|
| Rule 1 | Return-Path & Header Spoofing | Inspect raw headers for SPF, DKIM, and DMARC alignment passes. |
| Rule 2 | Unicode & Punycode Homoglyphs | Flag xn-- domain strings; type primary URLs manually via bookmarks. |
| Rule 3 | Deceptive Hyperlink Anchors | Hover to read true FQDN destination from right to left before clicking. |
| Rule 4 | Social Engineering & Fake Urgency | Verify emergency requests out-of-band via an independent, established channel. |
| Rule 5 | AiTM Reverse Proxy Interception | Deploy FIDO2/WebAuthn hardware keys and passkeys with cryptographic origin binding. |
Authoritative Standards & Industry References
- IETF RFC 7208 — Sender Policy Framework (SPF): Formal specification for email server IP authorization in DNS records.
- IETF RFC 6376 — DomainKeys Identified Mail (DKIM) Signatures: Cryptographic standard for message integrity verification.
- IETF RFC 7489 — Domain-based Message Authentication, Reporting, and Conformance (DMARC): The foundational protocol enforcing alignment between SPF and DKIM.
- Federal Bureau of Investigation (FBI) — Internet Crime Complaint Center (IC3) Annual Threat Report: Statistical analysis on business email compromise (BEC) and phishing attack patterns.
Sources & Further Reading
- FBI Internet Crime Complaint Center (IC3) — Annual Internet Crime Report — Official federal data on business email compromise (BEC), credential phishing losses, and emerging social engineering vectors.
- Cybersecurity & Infrastructure Security Agency (CISA) — Recognizing & Reporting Phishing Attacks — U.S. government guidance on identifying spoofed display names, malicious attachments, and credential-harvesting subdomains.
- IETF RFC 7208 — Sender Policy Framework (SPF) for Email Validation — Technical RFC standard explaining DNS-based reverse IP lookup authentication designed to prevent email sender spoofing.