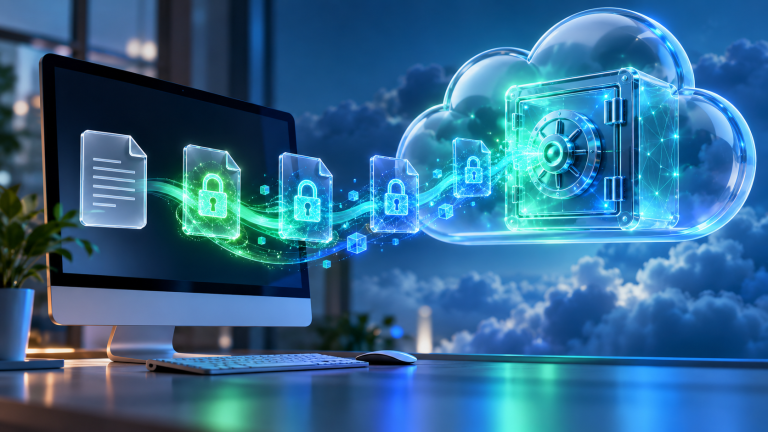
Cloud synchronization services like Google Drive, Microsoft OneDrive, and Dropbox are marvelous for real-time collaboration and cross-device file accessibility. However, none of these mainstream platforms offer default zero-knowledge client-side encryption. The service providers retain the master decryption keys to your files, exposing your tax returns, financial spreadsheets, and identity documents to internal staff snooping, government subpoenas, or automated content-scanning bots. Cryptomator bridges this gap by applying bulletproof client-side encryption directly on top of your existing cloud storage.
How Cryptomator Operates: The “Vault Inside Cloud” Architecture
Unlike full-disk encryption tools (like VeraCrypt) that create giant fixed-size container files that re-upload completely every time a single file changes, Cryptomator is engineered specifically for cloud synchronization:
- Per-File Encryption: Every file you place inside a Cryptomator vault is encrypted individually into an obfuscated ciphertext file.
- Metadata & Directory Obfuscation: File names, directory folder hierarchies, and file sizes are completely scrambled. A file named
passport_scan.pdfappears in your Google Drive as an unreadable scrambled file likea8f7c9e0-2b1d.c9r. - Bandwidth Friendly: If you edit a 20KB Word document inside a 50GB vault, your cloud sync client only uploads that single 20KB encrypted file.
Step 1: Installing and Creating Your First Encrypted Vault
- Download the open-source installer from the official Cryptomator website (available for Windows, macOS, Linux, Android, and iOS).
- Open Cryptomator and click Add Vault → Create New Vault.
- Provide a descriptive name (e.g., Secure_Cloud_Vault).
- When prompted for the storage location, select a folder directly inside your local Google Drive, OneDrive, or Dropbox synchronization directory.
- Set a strong Master Password. Cryptomator will generate a 24-word emergency recovery key. Print and store this recovery key safely; if you forget your password, Cryptomator developers cannot recover your data.
Step 2: Unlocking and Using Your Vault Like a Flash Drive
When you unlock your vault in Cryptomator by entering your password, it mounts as a virtual storage drive (e.g., Z: on Windows or a virtual volume in macOS Finder):
- Simply drag and drop sensitive files into this virtual drive exactly as you would with a physical USB flash drive.
- As you work, Cryptomator encrypts files on the fly in system memory using AES-256.
- When you lock the vault, the virtual drive vanishes. Your cloud provider syncs only the encrypted ciphertext blocks to remote servers.
Audited Open-Source Security
Cryptomator’s codebase is 100% open-source and has undergone comprehensive third-party cryptographic audits by Cure53 and other independent cybersecurity research firms, confirming zero backdoors and mathematically sound cryptographic implementation.